HPE GreenLake SSO with ClearPass
5 minute read
Single Sign-On with HPE GreenLake
Single Sign-On (SSO) allows users to access multiple applications and services using a single set of enterprise credentials. Instead of maintaining separate credentials for each application, authentication is delegated to a trusted Identity Provider (IdP). This provides users with a consistent authentication experience while allowing organizations to centrally enforce identity policies such as password requirements, multi-factor authentication, and account lifecycle controls.
HPE GreenLake supports enterprise SSO by integrating with external Identity Providers. For SAML-based SSO, HPE GreenLake operates as the Service Provider (SP) and redirects authentication requests to the organization’s configured IdP. After successfully authenticating the user, the IdP returns a signed SAML assertion containing the user’s identity and, depending on the authorization model, information used to determine the user’s access to GreenLake resources.
GreenLake supports two primary approaches for combining SSO authentication with authorization:
- Local authorization: The IdP authenticates the user, while user access, workspace membership, roles, and permissions are managed within GreenLake.
- Session-based authorization: The IdP performs authentication and provides authorization information in the SAML response. GreenLake dynamically assigns the user’s workspace and role access for the duration of the SSO session. GreenLake uses a configurable SAML attribute—by default
hpe_ccs_attribute—to carry this authorization information.
This architecture enables an organization to use HPE Aruba Networking ClearPass Policy Manager as the SAML Identity Provider, allowing ClearPass to authenticate users against enterprise identity stores and provide the SAML assertions required for access to HPE GreenLake.
GreenLake Configuration
The GreenLake configuration steps outlined here assume that you already have a GreenLake account and that you have claimed your domain. For information about claiming your domain, see Claiming a domain in HPE GreenLake.
This document focuses on the SSO connection and authentication policy configuration to work with ClearPass as the IdP.
Creating SSO Connection
- Log in to HPE GreenLake and navigate to Manage workspace > SSO Configuration > SSO connections > Create SSO connection

- Enter a name and select SAML 2.0 as the authentication protocol

-
Leave the defaults in the Map SAML attributes section
-
Copy and save the Entity ID, Destination URL and X.509 certificate from the identity provider configuration screen for use later in the ClearPass configuration

- After saving the GreenLake SSO information from the previous step, keep the GreenLake SSO configuration page open and, in a separate tab or browser, set up ClearPass as the IdP (refer to the ClearPass IdP Configuration section below). Once this is completed, you can download the CPPMIdPMetadata.xml file, which contains the ClearPass IdP information. Upload this metadata file to GreenLake

-
Set an appropriate session timeout value, then review and create the SSO connection
-
Once the SSO connection is created, select it and download the service provider metadata file from Actions > Download GreenLake metadata

Creating Authentication Policy
-
Log in to HPE GreenLake and navigate to Manage workspace > SSO Configuration > Authentication Policy > Create Authentication Policy
-
Select Verified domain and select the domain you claimed from the dropdown
-
Select the previously created SSO connection from the dropdown and set Authorization Mode to SSO role assignments


INFO
If the authorization mode is set to Local role assignments, users must be added to GreenLake and roles must be assigned locally in GreenLake. When using ClearPass as the IdP, it is recommended to use SSO role assignments, where the role and scope are returned from ClearPass in the hpe_ccs_attribute.
- Set up the recovery account, then review and create the authentication policy
ClearPass IdP Configuration
- Add an IdP web login page under ClearPass Guest > Configuration > Pages > Web Logins > Create a new web login page with Vendor Settings set to Single Sign-On - SAML Identity Provider

- Navigate to Policy Manager > Identity > Single Sign-On > Add Web Login Configuration and select the IdP web login page created in the previous step

- Select the Identity Provider (IdP) Signing Certificate and the Service Provider (SP) Signing Certificate. The SP signing certificate is the GreenLake X.509 certificate saved earlier (see step 4 of Creating SSO Connection). Select the appropriate certificates and click Save

- Once the ClearPass IdP configuration is done, export the IdP metadata file and return to step 5 of Creating SSO Connection in GreenLake
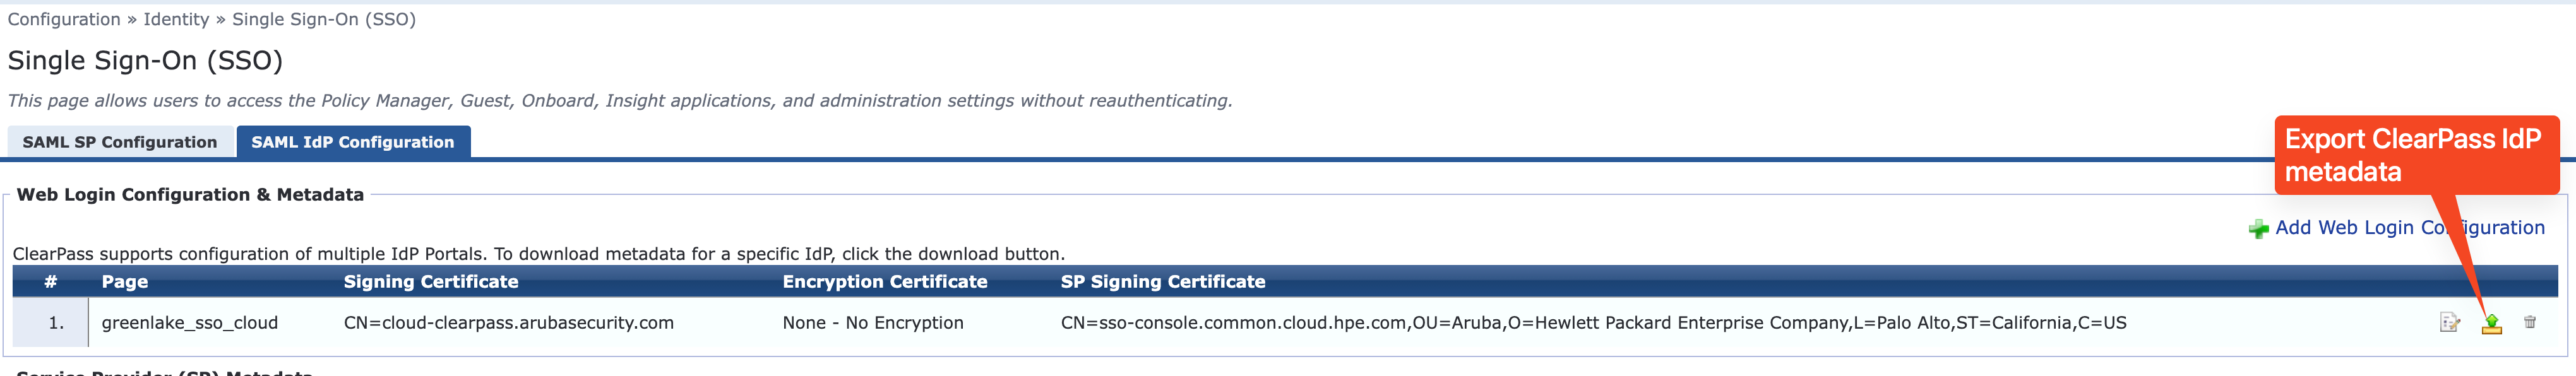
- Once the SSO connection configuration is done and the SP metadata has been downloaded, upload the metadata file under SAML IdP Configuration

ClearPass SSO Service Configuration
- Create a GreenLake SSO login enforcement profile from ClearPass Policy Manager > Configuration > Enforcement > Profiles, with the type set to Application

INFO
The hpe_ccs_attribute is a mandatory SAML assertion attribute used in HPE GreenLake single sign-on (SSO) configurations to define user authorization, workspace access, assigned service roles, and scope permissions.
The attribute value always starts with a version prefix followed by colon-delimited components mapping your platform customer ID, service application IDs, roles, and scope restrictions.
Details on building the hpe_ccs_attribute are documented in the HPE GreenLake Cloud User Guide.
- Create a SAML IdP authentication service from Configuration > Services > Add and select Aruba Application Authentication as the type
- On the Service tab, set the service condition
Application:SSO-SP EQUALS https://sso.common.cloud.hpe.com - The example below uses [Local User Repository] and Active Directory as authentication sources. Configure the appropriate authentication sources as required
- Configure the appropriate role mapping and enforcement profiles to assign different types of access based on the authorization lookups
